
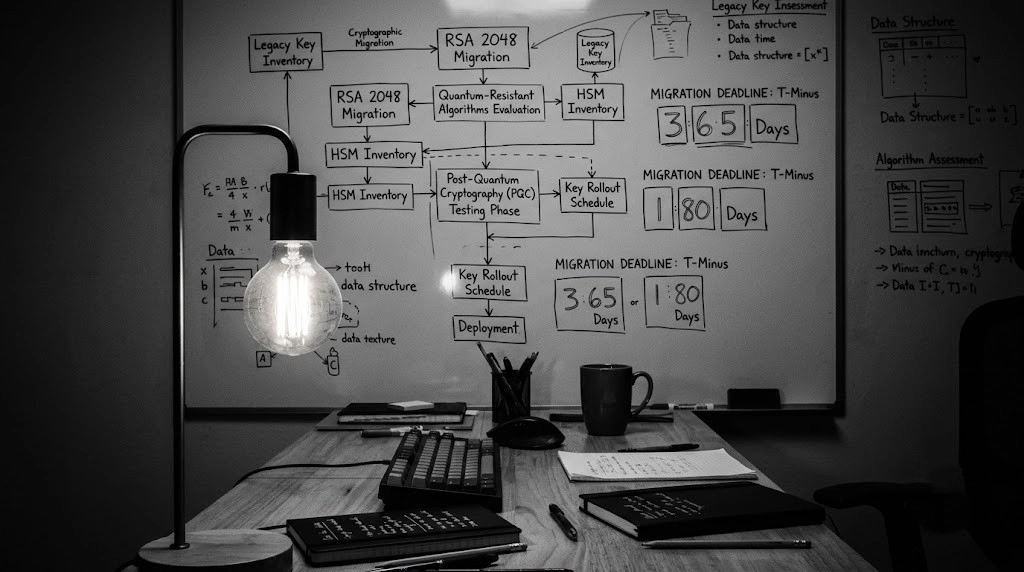
Post-Quantum Cryptography- The Clock Is Already Ticking for Small Businesses
A fintech founder I know spent three months last year getting SOC 2 certified. Tight process, real documentation, an auditor who actually pushed back. He was proud of it. Then I asked him one question: "Where does your product use RSA or ECC encryption?" He went quiet for a second. "Everywhere, I think. Why?"
That's the conversation most small businesses haven't had yet. And it needs to happen now — not in 2030, not after the next compliance cycle. Now.
why ?
What Actually Changed in August 2024
NIST finalized the first three post-quantum cryptography standards on August 13, 2024 — FIPS 203, FIPS 204, and FIPS 205 — ending an eight-year global evaluation process and triggering what analysts are calling the largest mandated cryptographic migration in history.
These three standards replace RSA and ECC — the 2 encryption systems that protect essentially every piece of sensitive data your business touches today. Your HTTPS connections, your API authentication, your customer data at rest, your signed documents, your payment flows. All of it runs on math that a sufficiently powerful quantum computer could break.
Wait — that sounds like a future problem, right?
Quantum computers capable of breaking RSA-2048 and ECC don't exist yet. But NIST's own guidance recommends organizations complete a full cryptographic inventory by 2025 and begin active migration well before 2030. The NSA's CNSA 2.0 mandate has already set hard deadlines for national security systems and government contractors.
hmm. "We'll deal with it when it's real" is precisely the strategy that fails here — because by the time a quantum computer capable of breaking RSA actually exists, the data it will decrypt was stolen years earlier. Attackers are harvesting encrypted data today. They'll decrypt it later. This attack already has a name: harvest now, decrypt later.
Why Small Businesses Are in the Crosshairs — Not Just Enterprises
Most SMB-facing coverage of post-quantum cryptography writes it off as an enterprise problem. Big companies, government contractors, critical infrastructure. Not you.
That framing misses something important.
OpenSSL Corporation's analysis puts SMB migration timelines at 3–4 years for discovery and planning alone, extending to 8–10 years for full completion depending on vendor readiness, SaaS reliance, and available budget.
If migration takes 3–4 years at minimum — and you haven't started — the math is straightforward. Starting in 2028 means you finish somewhere between 2031 and 2035. Regulatory pressure on private sector companies is expected to intensify between 2026 and 2028. Critical infrastructure companies face expected regulation between 2026–2028, and financial services companies between 2028–2032.
If your SaaS product touches healthcare, finance, legal data, or government clients — you are not watching this from a safe distance.
And honestly, most small businesses don't even know where RSA and ECC live in their stack. That's the starting problem. You can't migrate what you haven't mapped.
The "Harvest Now, Decrypt Later" Threat Is Already Operational
This is the part that changes the timeline from "future concern" to "current risk."
Nation-state adversaries — particularly those with long planning horizons — are already intercepting and storing encrypted communications at scale. The strategy is simple: collect everything encrypted today that might be valuable in 5 to 10 years, then decrypt it once quantum capability arrives.
The NIST migration timeline frames 2025 through 2027 as the active hybrid deployment phase — running classical and post-quantum algorithms in parallel. For most mid-market companies, this is the window they are currently in.
Here's the thing: the sensitivity of your data determines your urgency. A SaaS product storing customer health records has a very different risk profile than one storing anonymous usage analytics. Medical records collected today and decrypted in 2031 are still a HIPAA violation — and still damaging to the patient whose data they contain. The harm doesn't expire with the encryption method.
If you're building in healthtech, fintech, or anything touching personal data with a multi-year lifespan, "harvest now, decrypt later" is not theoretical. It is an active operational risk.
The SMB Migration Checklist — Where to Actually Start
Most post-quantum guidance was written for teams with a dedicated cryptographic engineer and 6 months of runway. The version for founders who need to make practical decisions without overhauling their entire infrastructure this quarter.
Step 1: Cryptographic inventory — know what you're running
Before you migrate anything, you need to know what you have. Map every place your product uses asymmetric encryption. TLS/HTTPS connections, API authentication tokens, JWT signing, S3 bucket encryption configuration, database-at-rest encryption, digital signatures on documents or code. Most SaaS stacks will have 8–15 distinct locations. Many founders have no idea they're using RSA in 6 of them because a library or cloud provider made that choice for them.
Step 2: Classify by data sensitivity and lifespan
Not everything needs to migrate on the same timeline. Sort your encryption use cases by two factors: how sensitive is the data, and how long does it need to remain private? Customer passwords with 90-day rotation schedules have a different risk profile than 10-year customer health records. Prioritise the high-sensitivity, long-lived data first.
Step 3: Check your vendor roadmaps — seriously
Most of your encryption probably isn't code you wrote. It's your cloud provider (AWS, GCP, Azure), your TLS library (OpenSSL, BoringSSL), your database encryption layer, your email provider's signing mechanism. The good news: these vendors are moving. AWS and Google Cloud have both published PQC roadmaps. NIST finalized ML-KEM (FIPS 203) for key exchange, ML-DSA (FIPS 204) and SLH-DSA (FIPS 205) for digital signatures — all approved for federal and commercial use as of August 2024. Most major cloud providers are tracking these standards. Check whether the libraries and services you rely on already support hybrid mode.
Step 4: Run in hybrid mode — not big-bang migration
Hybrid deployment means running classical and post-quantum algorithms in parallel, which is the approach NIST recommends for the 2025–2027 window. This is more practical for small teams because it doesn't require replacing everything simultaneously. Your TLS connections can negotiate post-quantum key exchange where both sides support it and fall back to classical where they don't. That's a much smaller operational risk than a full cutover.
Step 5: Document everything you find
This matters for two reasons. First, regulators asking about your cryptographic posture in a compliance audit will want to see that you have awareness and a plan — even if migration isn't complete. Second, your future self (or future security team) will thank you. A cryptographic inventory document created now is one of the highest-value security assets you can produce this year, and it costs almost nothing if done carefully.
The One Thing That Makes This Harder Than It Looks
Here's what nobody says clearly in the guides about post-quantum migration: the hardest part isn't choosing the right algorithm. It's finding all the places you need to change.
NIST finalized PQC standards in 2024, but most companies cannot even inventory where RSA and ECC live in their stack. Asymmetric cryptography is embedded in dependencies, cloud service defaults, third-party integrations, and infrastructure-as-code configurations that were set up years ago by someone who has since left the company.
This is why the migration timelines are measured in years, not months. The algorithms themselves are available. The discovery and refactoring work is what takes time — and it scales with the complexity and age of your codebase.
The businesses that start that discovery work in 2026 will have options when regulators start asking questions in 2028. The ones that start in 2029 will be racing a deadline with limited runway.
Post-quantum cryptography is not waiting for quantum computers to arrive before it becomes your problem. The data being collected today is the target. The migration timelines — 3 to 10 years depending on your stack — mean the clock started the moment NIST published those three standards in August 2024.
The practical starting point for any small business is the same: know what encryption you're running, classify it by data sensitivity, and check whether your vendors are already moving. Most of that work costs nothing but time. Waiting costs considerably more.
If you want a security architecture review that includes a cryptographic inventory as part of the scope — or if you want to know what your current public-facing stack exposes right now — the first step is a free scan at www.snippipedia.com, or you can reach out directly at www.snippipedia.com/contact.